
Network Penetration Testing vs Vulnerability Assessment: Which Approach Does Your Organisation Need?
Network penetration testing and vulnerability assessment are two complementary approaches that help organisations evaluate cyber risk. Although they share some techniques, their objectives, depth and deliverables differ.
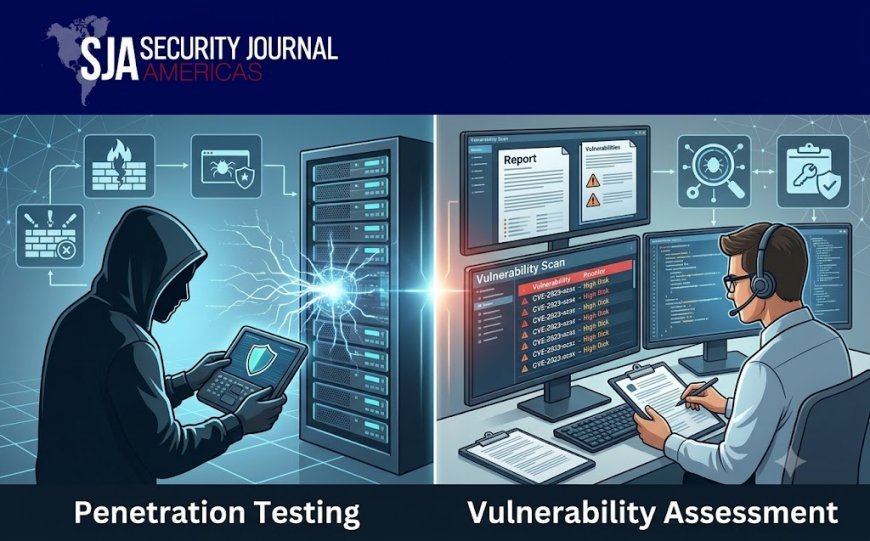
Understanding security weaknesses is essential for protecting business networks, but not every security assessment answers the same question. Some methods identify known vulnerabilities across systems, while others investigate whether selected weaknesses can be exploited and what consequences could follow. Network penetration testing and vulnerability assessment are two complementary approaches that help organisations evaluate cyber risk. Although they share some techniques, their objectives, depth and deliverables differ.
Understanding these differences allows security teams to select the right assessment for their needs and build a more effective security programme.
What Is a Vulnerability Assessment?
A vulnerability assessment is a systematic process for identifying, analysing and prioritising potential weaknesses in systems, devices and network infrastructure.
It often involves automated scanning, software version checks, configuration reviews and comparison against known vulnerability information. Results can help organisations discover outdated systems, insecure settings and missing security updates.
The primary objective is to establish visibility into potential weaknesses and provide a prioritised list of issues requiring attention.
Vulnerability assessments are particularly useful for organisations managing large numbers of devices because scanning can be repeated regularly to identify newly introduced problems.
However, a scanner may identify a possible weakness without determining whether it can be exploited in the organisation's specific environment.
What Is Network Penetration Testing?
Network penetration testing involves an authorised attempt to simulate selected attack techniques against systems within a defined scope. The objective is to evaluate how effectively network security controls prevent unauthorised access and protect important resources.
Testers may investigate exposed services, access restrictions, authentication mechanisms and network segmentation. They validate selected weaknesses using controlled techniques and assess the potential consequences.
Unlike a vulnerability scan that primarily identifies possible issues, a penetration test can demonstrate how certain weaknesses might be combined to create a more significant risk.
The assessment must remain within agreed boundaries and should avoid unnecessary disruption, destructive activity or exposure of sensitive information.
Comparing the Two Approaches
The key difference lies in the question each assessment answers.
A vulnerability assessment asks: Which potential security weaknesses exist, and which should be prioritised?
A penetration test asks: Can selected weaknesses be exploited within the approved scope, and what could that mean for the organisation?
Vulnerability assessments generally support broad and frequent coverage. Penetration tests usually require deeper investigation, specialist judgement and more careful control of testing activities.
Their outputs also differ. A vulnerability assessment typically produces a list of findings with severity ratings and recommended fixes. A penetration test provides evidence about validated weaknesses, possible attack paths and the effectiveness of relevant security controls.
Neither approach should be considered a complete substitute for the other.
When Should Businesses Choose a Vulnerability Assessment?
Vulnerability assessments are useful when organisations need to maintain an ongoing view of known security issues across extensive infrastructure.
They can support routine patch management, configuration reviews and prioritisation of weaknesses discovered through regular scanning.
For example, an organisation with hundreds of network devices may use recurring assessments to identify outdated software and confirm whether important security updates have been applied.
Regular scanning can also help security teams track changes in their vulnerability profile over time.
However, scan results should be reviewed carefully because automated tools may produce false positives or fail to capture risks that depend on interactions between systems.
When Is Penetration Testing More Appropriate?
Penetration testing is valuable when an organisation needs a deeper assessment of specific systems, security controls or potential attack paths.
It may be appropriate after major infrastructure changes, before introducing a sensitive service, following significant security improvements or when leadership needs evidence of how well particular controls perform.
Network penetration testing can also help evaluate whether a weakness in one part of a network could expose another area containing sensitive information.
Testing should be planned according to business risk, operational constraints and the criticality of the systems involved.
Why Combining Both Methods Produces Better Results
A strong security programme uses vulnerability assessments and penetration tests for different purposes.
Regular vulnerability scanning can identify emerging issues and help teams prioritise routine maintenance. Periodic penetration testing can then examine selected risks in greater depth and evaluate whether important safeguards work as intended.
For example, a scan may reveal an outdated network service. A controlled penetration test may establish whether that service creates a realistic route to a protected system. Together, the findings provide a more complete picture of exposure.
For the audience of Security Journal Americas, the practical message is to align each assessment with a clear security objective rather than choosing one method exclusively.
Measuring Results and Improving Security
Both approaches require effective remediation. Findings should be assigned to responsible teams, prioritised according to business impact and tracked until corrective action is verified.
Organisations should monitor recurring vulnerabilities, remediation times, unresolved high-risk findings and the outcomes of retesting. These measures can reveal whether the security programme is improving.
Network penetration testing should contribute to this broader process by helping validate whether important weaknesses have been addressed and whether relevant controls continue to perform effectively.
Conclusion
Vulnerability assessments provide broad visibility into potential weaknesses, while penetration tests investigate selected risks through controlled attack simulations. Both approaches offer important but different insights.
By combining regular scanning with risk-based network penetration testing, organisations can improve vulnerability management, validate critical security controls and make better-informed decisions about protecting their networks.
Frequently Asked Questions
1. Is a vulnerability assessment the same as penetration testing?
No. A vulnerability assessment identifies and prioritises potential weaknesses, while penetration testing validates selected weaknesses and evaluates their possible consequences.
2. Which approach is more cost-effective?
It depends on the scope and objectives. Automated assessments can support frequent, broad coverage, while penetration testing provides deeper investigation of selected risks.
3. Can vulnerability scanning replace penetration testing?
No. Scanning is useful for identifying known issues but may not reveal how weaknesses interact or whether particular attack paths are viable.
4. How often should vulnerability assessments be performed?
Frequency should reflect risk, infrastructure size, system changes and the organisation's security requirements.
5. Should small businesses conduct penetration testing?
Yes, when appropriate to their risk profile. The scope can be tailored to their most important systems, sensitive information and potential exposure.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0